



U.S. defense personnel data agency hit by security breach affecting 3 million
The U.S. Defense Manpower Data Center reported a significant data security incident that compromised the sensitive personal information of approximately 3 million people.


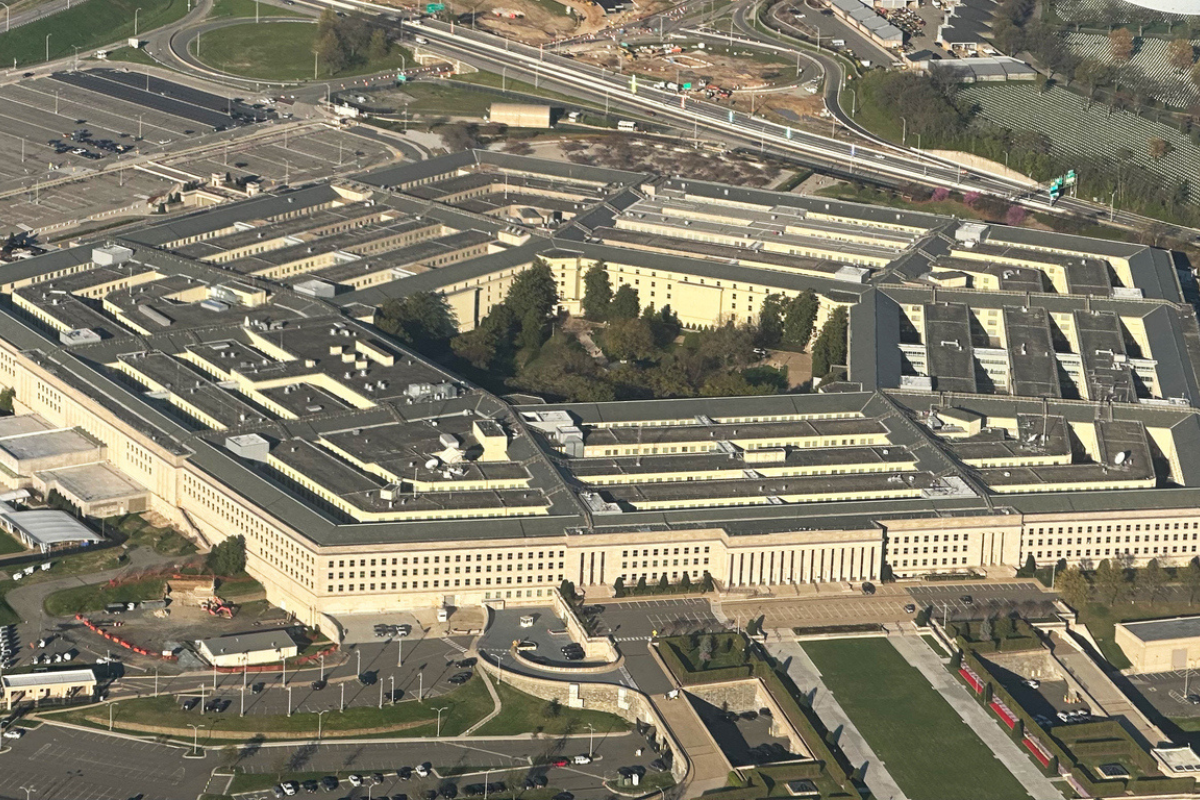
The U.S. Defense Manpower Data Center has suffered a major data security breach that exposed the sensitive personal information of approximately 3 million individuals.
The Defense Manpower Data Center (DMDC) is a central support organization and data repository within the U.S. Department of Defense. It serves as a major hub for manpower, personnel, training, benefits, and financial data, maintaining more than 60 million active and historical records on service members, civilian employees, contractors, veterans, retirees, and military families. DMDC also manages critical systems such as the Defense Enrollment Eligibility Reporting System (DEERS), which is used to verify eligibility for military healthcare and other benefits.
In a data security incident notice sent to affected individuals, the DMDC said that on July 16, it identified a security vulnerability in its file-sharing system that allowed unauthorised users to access confidential files. The organisation immediately launched an investigation to determine the nature and scope of the incident.
It also promptly updated the file sharing system to patch the vulnerability and restored the affected system.
“Analysis identified that between October 2025 and the date of discovery, a small number of unauthorised users accessed files on a server containing unencrypted PII,” reads the letter sent to affected individuals.
The compromised data included individuals’ names, dates of birth, Social Security numbers, contact information, sex, race, and military personnel information. While the DMDC did not disclose the number of affected individuals, CNN reported that the Pentagon confirmed the breach impacted approximately 2.76 million living individuals and 294,000 deceased individuals.
“Upon discovery of the security vulnerability, DMD immediately initiated privacy and cybersecurity incident response actions in accordance with Office of Management and Budget and Department guidelines and policies. We are taking appropriate actions to assess and enhance the cybersecurity posture of the DMDC system,” the organisation added.
DMDC has urged affected individuals to remain vigilant by regularly reviewing their credit reports, account and benefits statements, and to report any suspicious activity to law enforcement agencies, including local police and the state attorney general.
It has also offered one year of complimentary credit monitoring services through IDX to all affected individuals.
At the time of publication, no known hacker group had claimed responsibility for the breach of DMDC’s internal network, and the Pentagon had not disclosed any details about the intruders.
Your Next Read
Related Articles
Teiss Talk

Closing the exposure window — unifying continuous threat exposure management

Trusting your AI agents

The blind spots in your stack - why fragmented data security fails

Winston House, 3rd Floor,
Units 306-309, 2-4 Dollis park,
London, N3 1HF
020 8349 4363
© 2026, Lyonsdown Limited. teiss® is a registered trademark of Lyonsdown Ltd. VAT registration number: 830519543