


Trezor discloses data breach affecting nearly 14,000 customers after shipping partner hack
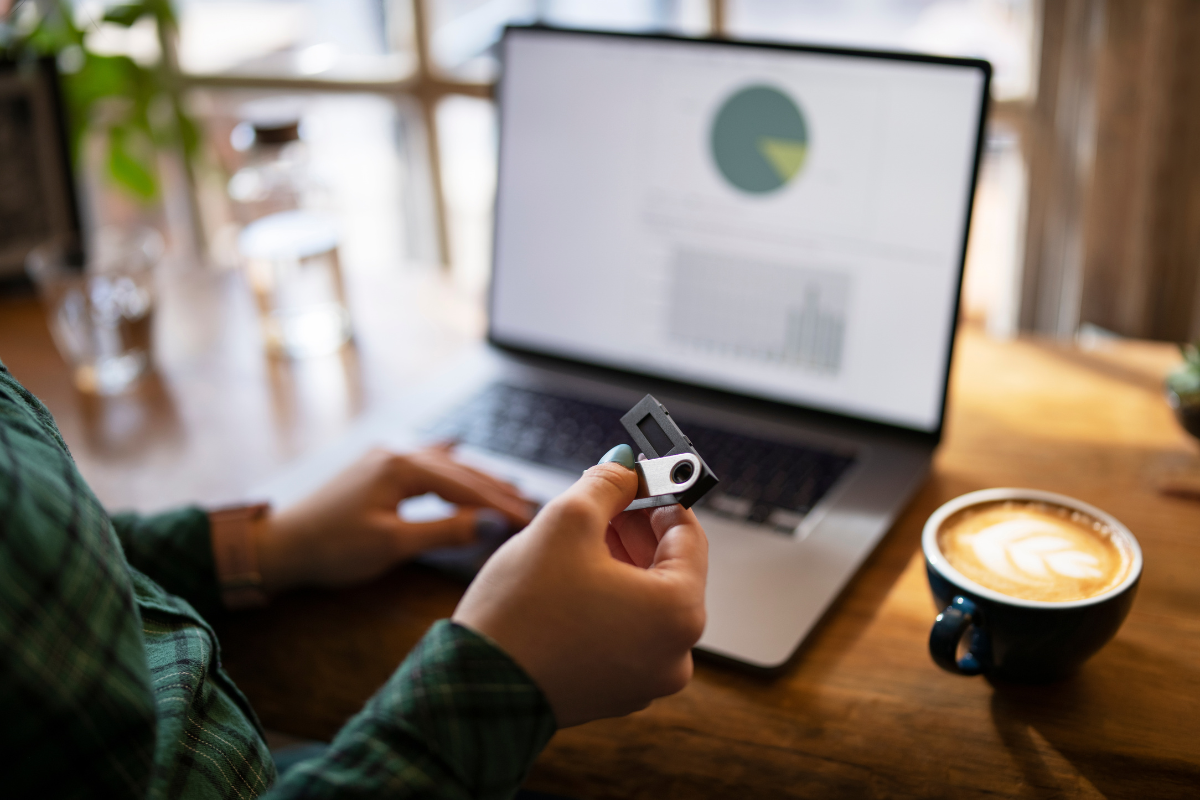
Hardware cryptocurrency wallet maker Trezor has disclosed a data breach affecting close to 14,000 customers after its shipping and logistics partner, ShipMonk, suffered an unauthorized intrusion into its systems.
Trezor said the exposed information included customers’ full names, shipping addresses, email addresses, and phone numbers, all tied to order records handled by ShipMonk. In a blog post published Thursday, the company said the breach touches customers located in the United States, the United Kingdom, Sweden, Colombia, Brazil, Italy, and Portugal who placed orders between May 10 and August 8, 2026.
Trezor said ShipMonk alerted it on Monday, August 10, 2026, to the unauthorized access of systems holding customer data. According to the company, 11,742 customers had their name, email, phone number, and shipping address fully exposed, while another 1,947 customers experienced partial exposure limited to name, city, and email.
The company said its own operations and services were not affected, that its internal systems remained secure, and that customer devices were not compromised as a result of the incident. Trezor cautioned affected customers to be alert to unsolicited messages seeking personal details, warning that phishing attempts could increase in the aftermath of the breach.
"To be clear, our systems were not compromised, and your Trezor device is secure, but the affected customers might be targeted by more sophisticated phishing attempts," Trezor said, adding that scammers could use the leaked data to send fraudulent emails, place deceptive phone calls, mail fake letters, or pose as banks, cryptocurrency exchanges, or Trezor itself.
Trezor did not detail how ShipMonk’s systems were compromised. However, in breach notification emails sent to affected customers and reviewed by BleepingComputer, ShipMonk said the attackers exploited a vulnerability in Metabase, a third-party analytics platform it uses. ShipMonk said Metabase informed it on August 6, 2026, that an unauthorized party had exploited a flaw in Metabase’s software to access data tied to ShipMonk’s account and its customers. ShipMonk said that, based on representations from Metabase, the vendor has since patched the vulnerability and invalidated all active sessions, and that it launched a technical investigation with outside information technology experts.
This is not Trezor’s first disclosed breach. In January 2024, the company reported a separate incident in which threat actors accessed its third-party support ticketing portal, exposing the names, usernames, and email addresses of roughly 66,000 users who had interacted with Trezor Support since December 2021. Following that breach, Trezor confirmed the stolen data was used in phishing attacks designed to trick recipients into revealing the 24-word recovery seed phrases issued when setting up their wallets.
Your Next Read
Related Articles
Teiss Talk
Building cyber-resilience across your digital supply chain
Closing the exposure window — unifying continuous threat exposure management

Winston House, 3rd Floor,
Units 306-309, 2-4 Dollis park,
London, N3 1HF
020 8349 4363
© 2026, Lyonsdown Limited. teiss® is a registered trademark of Lyonsdown Ltd. VAT registration number: 830519543