



RNLI warns supporters of possible data breach as it faces far-right targeting
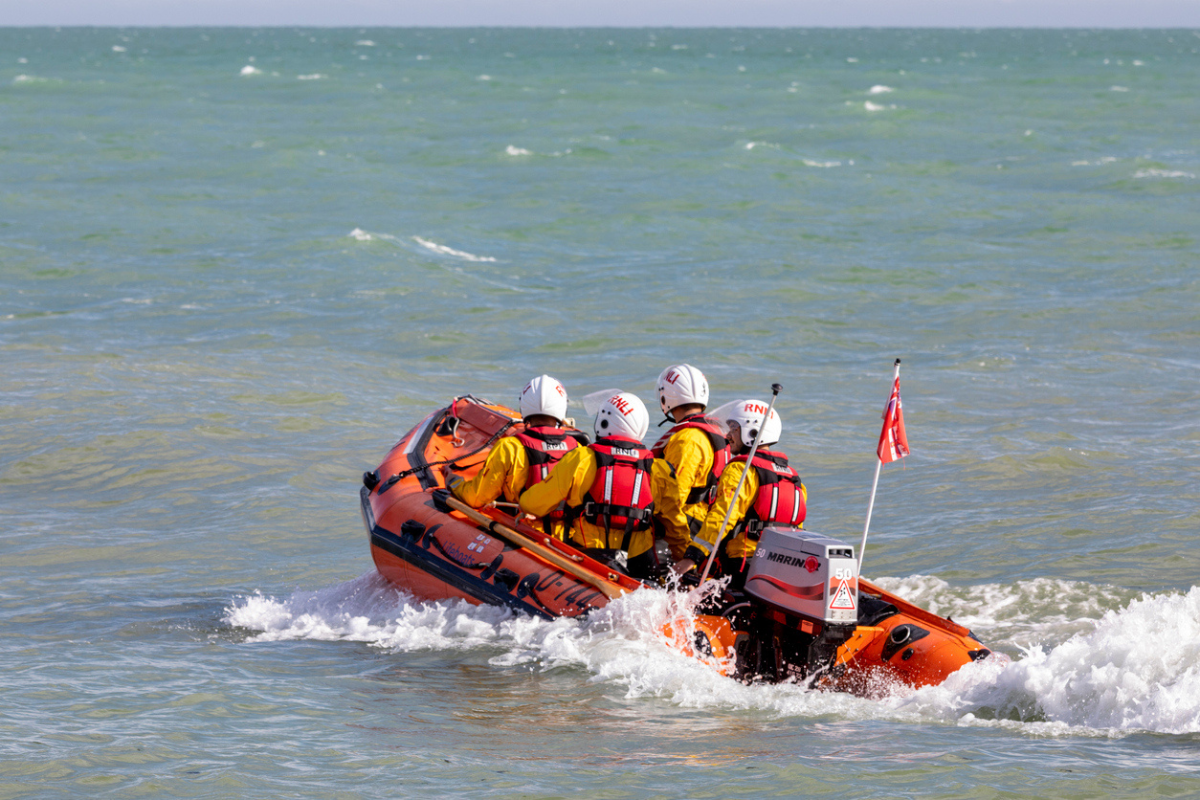
The Royal National Lifeboat Institution has told supporters that their personal information may have been stolen in a cyberattack on Beacon CRM, the customer-relationship-management provider it uses, days after RNLI volunteers were targeted online and in person by far-right protesters angry over the charity’s rescues of migrants crossing the English Channel.
In a letter accompanying the autumn edition of its Lifeboat magazine, the RNLI warned members that hackers may have accessed their names, contact details and records of their interactions with the charity. The Telegraph first reported the disclosure, saying Beacon CRM had advised the RNLI to assume that data held within its systems had been taken in a cyberattack that affected about 1,500 charities in late July. A report published by Beacon CRM this month said there was no evidence the attack targeted Beacon or any specific customer, and that the attacker had told the company it would delete any data it had exfiltrated and would not retain, sell or share copies.
An RNLI spokesperson said Beacon CRM could not confirm exactly which records were accessed or downloaded, but had advised all affected organizations, including the RNLI, to assume their data had been taken. The charity said there is no evidence to date that supporters’ information has been published, shared online or otherwise misused.
The breach disclosure comes after RNLI volunteers faced abuse tied to the charity’s search-and-rescue work. On Sept. 6, activists tried to blockade a road leading to a landing spot in Eastney, Portsmouth, where two RNLI crews helped bring a dinghy carrying about 120 asylum seekers to shore; police officers were injured in the ensuing clashes. In the following days, lifeboat crew members were called traitors online, protests took place outside the RNLI’s headquarters in nearby Poole, and a museum there closed temporarily. The Portsmouth lifeboat station took down its Facebook page and was temporarily shut, and volunteers across the U.K. were told to consider not wearing the charity’s branded clothing if they felt it could put them at risk.
RNLI vice-president Sir Robin Knox-Johnston condemned the intimidation of staff and volunteers, including online and physical abuse, calling it "frankly quite disgraceful." Chief executive Peter Sparkes called the abuse "wholly unacceptable in civilized society," adding that the RNLI works to save lives at sea regardless of whose lives they are. The charity said it experienced a significant boost to fundraising after far-right protesters called for a donation boycott, and it noted that only 1.2% of its rescue callouts last year, 109 of 9,058, involved small boats in the Channel.
Dr. William Allchorn, a senior research fellow at Anglia Ruskin University’s International Policing and Public Protection Research Institute, said the data breach could be exploited by far-right activists already using open-source maritime tracking tools, adding that the exposure could create a "chill effect" that gives fringe elements of the movement key information about volunteers.
Your Next Read
Related Articles
Teiss Talk

Closing the exposure window — unifying continuous threat exposure management

Trusting your AI agents

The blind spots in your stack - why fragmented data security fails

Winston House, 3rd Floor,
Units 306-309, 2-4 Dollis park,
London, N3 1HF
020 8349 4363
© 2026, Lyonsdown Limited. teiss® is a registered trademark of Lyonsdown Ltd. VAT registration number: 830519543