



McKesson’s data breach impacted over 6.4 million accounts, says Troy Hunt
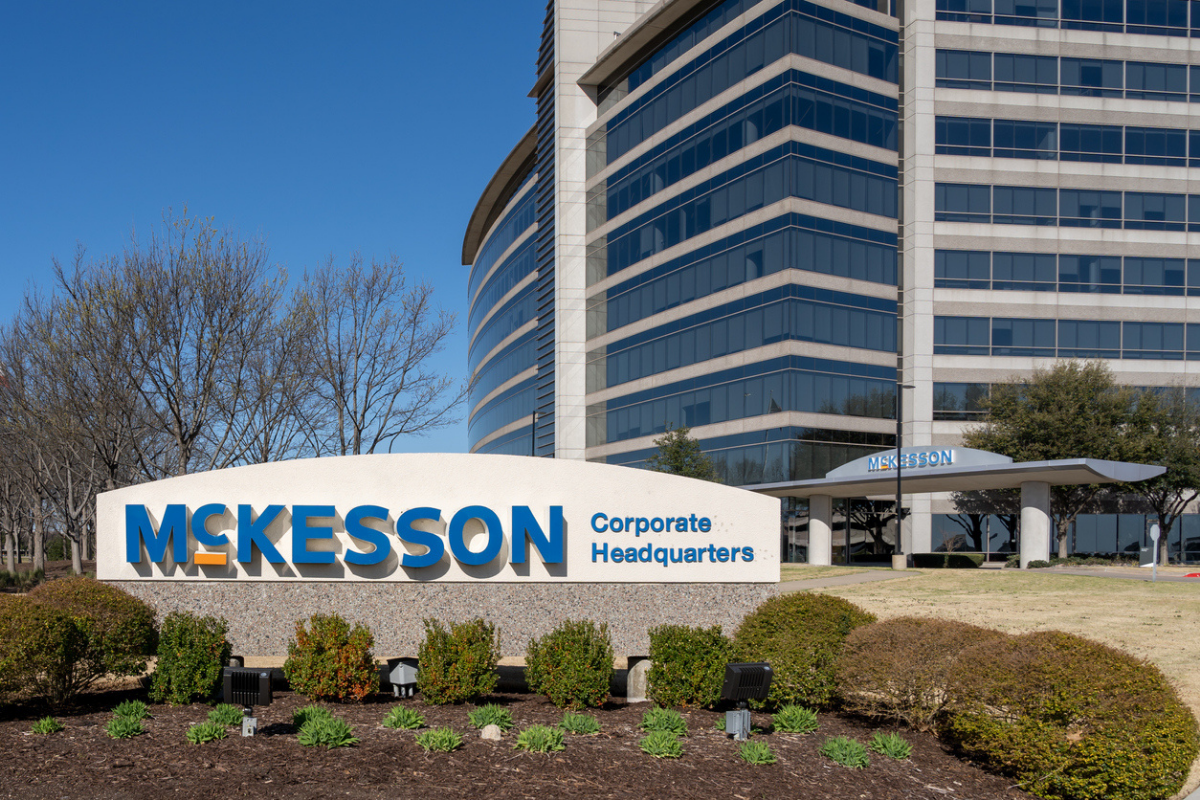
Security researcher Troy Hunt reported that the McKesson data breach exposed information from approximately 6.4 million user accounts.
In a SEC filing, McKesson revealed that hackers had gained unauthorised access to several of its cloud-based accounts and removed company data. The company detected the intrusion on August 25 and promptly initiated an investigation to assess the nature and extent of the breach. In a statement published on its website, McKesson also warned that the cyber incident could lead to intermittent service disruptions.
The ShinyHunters hacking group claimed responsibility for the cyber attack on McKesson and said it had stolen approximately 284 million records over a period of four days. According to the group, the attackers gained access to the targeted systems by using voice-phishing techniques to deceive employees and obtain the information or access credentials needed to carry out the attack.
The hackers claimed they accessed millions of patient records through McKesson’s Snowflake and Salesforce cloud environments, though the exact number of affected individuals remains unclear. The stolen information included names, addresses, Social Security numbers, and sensitive medical details such as diagnoses, medications, allergies, and patient notes. Personal data of employees was also affected during the incident.
ShinyHunters has demanded a $55 million ransom from the company, giving it 72 hours to make the payment in exchange for keeping the stolen data private. If the ransom is not paid within that deadline, the group has threatened to publicly release the database.
Troy Hunt, security researcher and creator of Have I Been Pwned, analysed the newly published database and confirmed that the breach exposed 6.4 million accounts. The compromised data included names, dates of birth, addresses, email addresses, phone numbers, employers information, personal health data and more.
“The impacted data related to a range of individuals and roles, including marketing campaign recipients, patients, staff, and healthcare provider contacts,” HIBP added.
Your Next Read
Related Articles
Teiss Talk

Closing the exposure window — unifying continuous threat exposure management

Trusting your AI agents

The blind spots in your stack - why fragmented data security fails

Winston House, 3rd Floor,
Units 306-309, 2-4 Dollis park,
London, N3 1HF
020 8349 4363
© 2026, Lyonsdown Limited. teiss® is a registered trademark of Lyonsdown Ltd. VAT registration number: 830519543