


McKesson investigates breach after ShinyHunters claims patient data theft
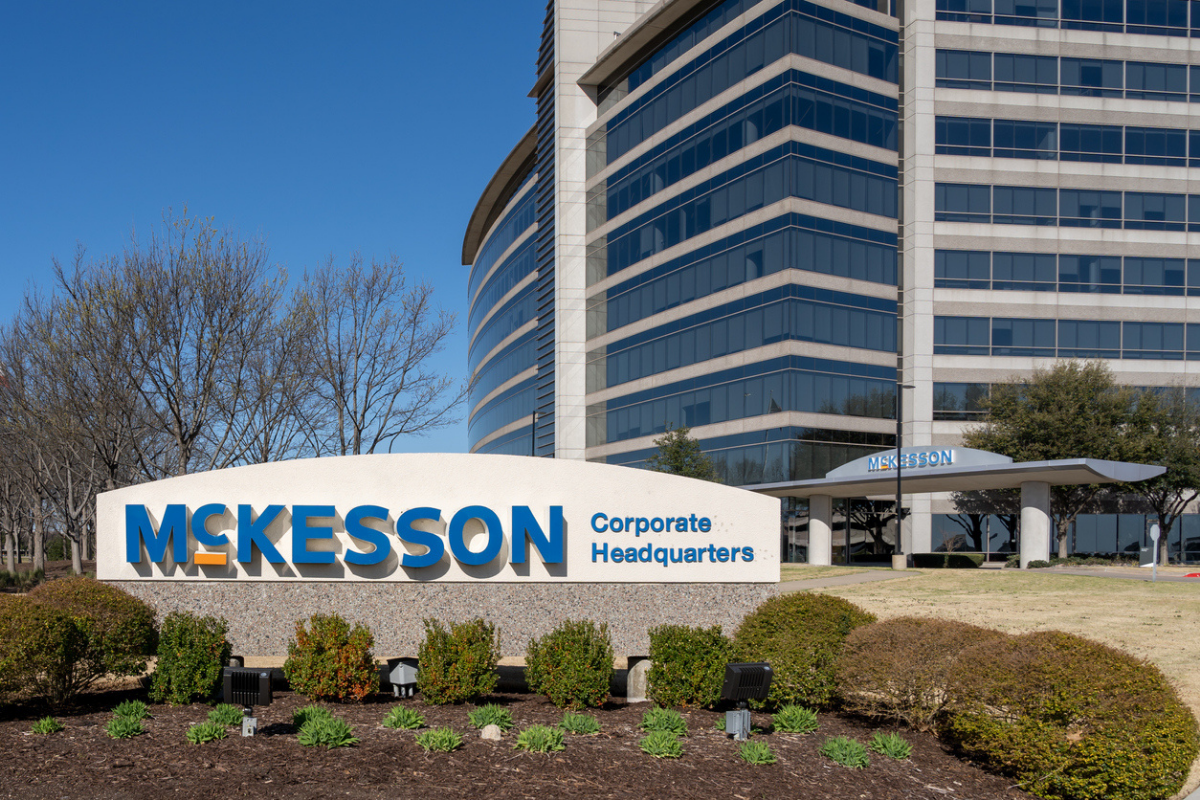
McKesson Corporation recently disclosed a data security incident after the ShinyHunters hacking group claimed to have breached its internal network and stolen confidential patient information.
Headquartered in Irving, Texas, McKesson is a major healthcare company supplying pharmaceuticals, medical and surgical products, and technology services to healthcare providers across North America. It also supports medication access and cancer care through platforms such as CoverMyMeds and specialised oncology services.
In a filing with the U.S. Securities and Exchange Commission (SEC), McKesson said that on August 25, it detected an unauthorised intrusion into its network. The company promptly initiated an investigation, supported by external cyber security specialists, to assess the nature and extent of the breach.
In a statement published on its website, McKesson revealed that hackers had gained unauthorised access to several of its cloud-based accounts earlier in the week and removed company data. The company also warned that the cyber incident could lead to “intermittent service disruptions.”
McKesson Chief Technology Officer, Francisco Fraga added that the compromised information was associated with the company’s oncology and multi-specialty, as well as medical-surgical, business units.
“As of the date of this filing, the company has not determined that the incident is material or that the incident has had, or is reasonably likely to have, any material impact on the company, including its financial condition or results of operations,” McKesson added.
‼️🇺🇸 ShinyHunters claims a U.S.-based financial technology.
— Dark Web Informer (@DarkWebInformer) August 28, 2026
🇺🇸 Jack Henry & Associates - A U.S.-based financial technology company providing core banking, payment processing, digital banking, and other technology services to banks and credit unions. pic.twitter.com/mYepD91ksx
The ShinyHunters hacking group claimed responsibility for the cyber attack on McKesson and said it had stolen approximately 284 million records over a period of four days. According to the group, the attackers gained access to the targeted systems by using voice-phishing techniques to deceive employees and obtain the information or access credentials needed to carry out the attack.
The hackers claimed they accessed millions of patient records through McKesson’s Snowflake and Salesforce cloud environments, though the exact number of affected individuals remains unclear. The stolen information included names, addresses, Social Security numbers, and sensitive medical details such as diagnoses, medications, allergies, and patient notes. Personal data of employees was also affected during the incident.
ShinyHunters has demanded a $55 million ransom from the company, giving it 72 hours to make the payment in exchange for keeping the stolen data private. If the ransom is not paid within that deadline, the group has threatened to publicly release the database.
Your Next Read
Related Articles
Teiss Talk


Building cyber-resilience across your digital supply chain

Closing the exposure window — unifying continuous threat exposure management

Winston House, 3rd Floor,
Units 306-309, 2-4 Dollis park,
London, N3 1HF
020 8349 4363
© 2026, Lyonsdown Limited. teiss® is a registered trademark of Lyonsdown Ltd. VAT registration number: 830519543