


Cyberattack disrupts operations at North Carolina's ports, forces manual gate processing
The North Carolina Ports Authority is still restoring systems days after an IT outage slowed cargo operations at two seaports and an inland hub.


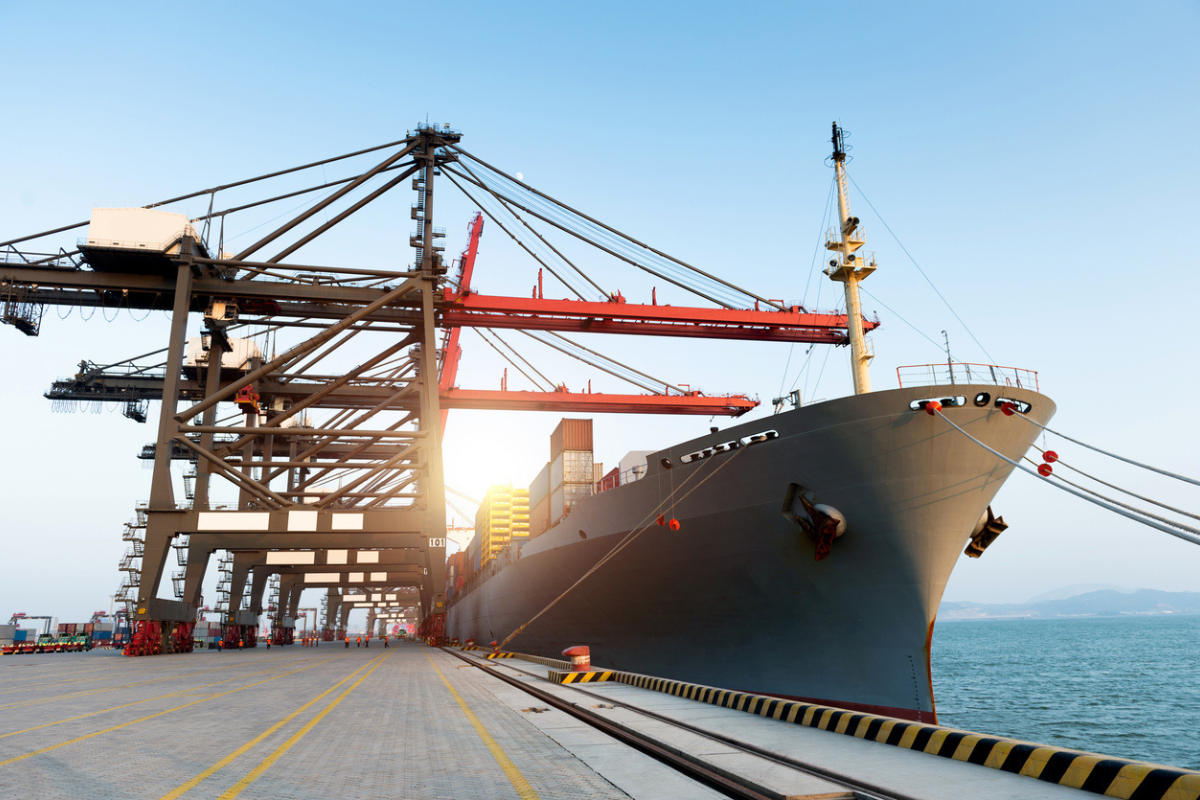
The North Carolina Ports Authority has confirmed that a cyberattack disrupted IT systems and slowed operations at the Port of Wilmington, the Port of Morehead City and the Charlotte Inland Port, forcing crews to shift to manual processing at gates across all three facilities. The attack was reportedly detected on August 4, prompting the authority to activate its cybersecurity contingency plan and begin recovery efforts the following morning.
The three sites together make up the state’s port system, combining two deepwater seaports with an inland logistics hub. The Port of Wilmington is the largest of the three, operating nine berths with an annual container capacity of 600,000 twenty-foot equivalent units and averaging 5,000 container gate moves each week. Wilmington and Morehead City together move 4.4 million short tons of bulk and breakbulk cargo annually, making the pair significant hubs for regional freight movement.
The systems-wide outage forced gates at all three locations to open at 8 a.m. on August 5, delaying operations for the ports and the trucking companies that rely on them. The authority has not attributed the attack to any known threat actor and has not said whether sensitive data was stolen. No hacking group had publicly claimed responsibility as of this report.
A status update posted to the port authority’s website said normal gate schedules were expected to resume the following day. "Gates at the Port of Wilmington, the Port of Morehead City, and the Charlotte Inland Port will follow a normal operating schedule tomorrow, August 7," the update read, adding that vessel activity would also proceed as scheduled. "As our IT team continues assessing affected systems and restoring services, delays can be expected. We appreciate your patience." The authority said operations were gradually returning to normal but cautioned that further delays should be expected while restoration work continues.
The disruption centered on a systems-wide IT outage that pushed all three facilities into manual gate processing. Authorities activated the Cybersecurity Contingency Plan immediately after detection and brought in state and federal partners to assist with the response. No technical indicators of compromise, malware samples or forensic details have been made public, and there is no evidence to date of ransomware deployment, data theft or impact to operational technology systems. The observed disruption is consistent with a denial-of-service-style technique, though a fuller technical assessment has not been possible without additional forensic evidence. The disruption pattern resembles previous cyberattacks that have hit port and logistics operators elsewhere, though officials caution that comparison remains circumstantial without confirmed technical indicators.
Officials and security analysts have pointed to the incident as a reminder that operators of critical logistics infrastructure need contingency plans that are regularly tested and paired with close coordination between state and federal agencies. Recommended steps following incidents of this kind include maintaining network segmentation and access controls to contain outages, keeping documented manual fallback procedures ready for deployment, and running regular tabletop exercises to identify gaps in incident response.
Your Next Read
Related Articles
Teiss Talk


Building cyber-resilience across your digital supply chain

Closing the exposure window — unifying continuous threat exposure management

Winston House, 3rd Floor,
Units 306-309, 2-4 Dollis park,
London, N3 1HF
020 8349 4363
© 2026, Lyonsdown Limited. teiss® is a registered trademark of Lyonsdown Ltd. VAT registration number: 830519543